Showing posts with label oracle access manager. Show all posts

Monday, April 17, 2017

OAM: Enable White Listing mode

                       We are going to cover about the commands that can be used to enable White listing of URLs in OAM and enable it on OAM Protected applications. This white listing of URLs helps to avoid re-directions to external sites/URLs that are not registered with OAM.

Environment:
  • OAM 11.1.2.3BP07
  • RHEL6/OEL6
Steps:

      Enabling and configuring White-listing  mode is very simple and just requires the following acitivites.
  1. Enable OAM White listing Mode
  2. Adding/Removing URLs to/from the list of White listed URLs
1. Enable OAM White listing Mode:
  • Login to the server that contains installation of OAM component
  • Browse to the following directory
    • <Oracle_IDM_Home>/common/bin
  • Execute the following commands
    • ./wlst.sh
    • connect('weblogic','password','t3://oamhost:7001'>)
    • domainRuntime()
    • oamSetWhiteListMode(oamWhiteListMode="true")
  • This returns the success message as shown below.
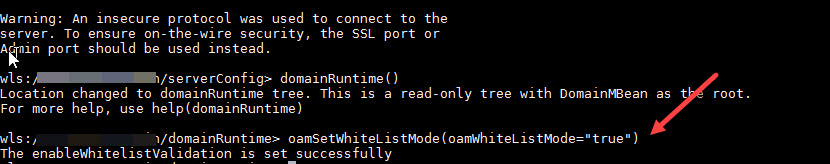
2. Adding/Removing URLs to/from the list of White listed URLs :
  • Execute the below command to add a URL to the list
    • oamWhiteListURLConfig(Name="google",Value="http://www.google.com",Operation="Update")  


  • Execute the below command to remove a URL from the list
    • oamWhiteListURLConfig(Name="google",Value="http://www.google.com",Operation="Remove") 


Validation:
  • We can validate the behaviour during the logout process of any protected application with OAM Logout URL. For example, Add a URL like "http://www.google.com/" to white list and  invoke the following Logout URL which has end_url parameter with the google.com URL
    • http://<OHSHost:7777/oamsso/logout.html?end_URL=http://www.google.com/
  • After successful logout, above URL will redirect you back to "http://www.google.com/" as it is trusted URL.
  • You can validate by removing the same URL from the White Listed URLs list and invoke logout again. Then OAM will just log you out but will not redirect the user to "http://www.google.com/"
Thanks for visiting.

Wednesday, April 12, 2017

OAM: Storage not configured error in Session Management

               Receiving "Storage not configured" error popup in OAM console while accessing user session management information.  


Environment:
  • OAM 11.1.2.3 BP07
  • RHEL6/OEL6
  • OUD 11.1.2.3
Cause:

OAM Console throws "Storage not configured" error due to couple of reasons. This might happen
  • If there is no single OAM managed server up and running.
  • When Admin server failed to initialize session manager with the following exception in Admin logs
<Oct 12, 2016 7:06:41 PM EDT> <Warning> <oracle.oam.admin.console.policy> <BEA-000000> <Exception in getting sessionmanager
oracle.security.am.engines.sme.exceptions.ManagerNotCreatedException: OAMSSA-02008: Cannot instantiate the persistence access implementation for class PersistedSessionCache.

        at oracle.security.am.engines.sme.mgr.AbstractSessionManager.handleInstantiationFailure(AbstractSessionManager.java:325)
        at oracle.security.am.engines.sme.mgr.AbstractSessionManager.<init>(AbstractSessionManager.java:306)
        at oracle.security.am.engines.sme.mgr.SessionManagerImpl.<init>(SessionManagerImpl.java:51)
        at oracle.security.am.engines.sme.mgr.SessionManagerImpl.getInstance(SessionManagerImpl.java:66)
        at sun.reflect.NativeMethodAccessorImpl.invoke0(Native Method)
        at sun.reflect.NativeMethodAccessorImpl.invoke(NativeMethodAccessorImpl.java:57)
        at sun.reflect.DelegatingMethodAccessorImpl.invoke(DelegatingMethodAccessorImpl.java:43)
        at java.lang.reflect.Method.invoke(Method.java:606)
        at oracle.security.am.engines.sme.SessionManagerFactory.getManager(SessionManagerFactory.java:281)
        at oracle.security.am.engines.sme.SessionManagerFactory.readObject(SessionManagerFactory.java:207)
        at oracle.security.am.engines.sme.SessionManagerFactory.getSessionManager(SessionManagerFactory.java:95)
        at model.SessionSearchVOImpl.executeSMESearch(SessionSearchVOImpl.java:410)
        at model.SessionSearchVOImpl.retrieveResultSet(SessionSearchVOImpl.java:602)
        at model.SessionSearchVOImpl.executeQueryForCollection(SessionSearchVOImpl.java:324)
        at oracle.jbo.server.ViewRowSetImpl.execute(ViewRowSetImpl.java:1282)
        at oracle.jbo.server.ViewRowSetImpl.executeQueryForMasters(ViewRowSetImpl.java:1509)
        at oracle.jbo.server.ViewRowSetImpl.executeQueryForMode(ViewRowSetImpl.java:1415)
        at oracle.jbo.server.ViewRowSetImpl.executeQuery(ViewRowSetImpl.java:1400)
        at oracle.jbo.server.ViewObjectImpl.executeQuery(ViewObjectImpl.java:7672)
        at oracle.adf.model.bc4j.DCJboDataControl.executeIteratorBinding(DCJboDataControl.java:1346)
        at oracle.adf.model.binding.DCIteratorBinding.doExecuteQuery(DCIteratorBinding.java:2265)


Fix:

Following actions can help in the fixing the issue.
  • Make sure to start the OAM Managed server before accessing the Session Management information through OAM Admin console
  • If the above action doesn't work, Restart the OAM Admin Server(Weblogic Admin Server) again after having the OAM Managed server Up and Running.
Thank you for visiting.

Tuesday, February 21, 2017

Salesforce SSO with OAM PS3 (11.1.2.3) [Part-2]

  • Click on 'Federation' and Go to 'Identity Provider administration'
 
  • Click on 'Create Service Provider Partner'
  • Click on 'browse' in Service information section and import the sp_metadata.xml file
  • Also provide the name and description of this partner profile
 
  • This will populate all the below details of service provider
    • providerid (Note: This is required while building this url for sso)
    • signing certificate and validity
  • Scroll down and update NameID format as below
    • NameID Format: Unspecified (SAML Subject NameID policy)
    • NameID value: UserID Store Attribute => mail  (OUD attribute name from which subject has to be populated)
  • Click on Save. This will finish the creation of Service provider partner profile on OAM side as shown below.
Test data setup in IDP and SP:
  • Lets create a test user profile on IDP authentication provider which is OUD in our lab.
  • Similarly create a user profile on salesforce side with same email as username.
 
Validation:
  • Finally now let's validate the single sign-on to salesforce
  • Now build the OAM protected federation url as below and access it.
    • http://<ohs_host:ohsport>/oamfed/idp/initiatesso?providerid=<SP_partner_providerid>
  • From my environment, below is the URL
    • http://dev.fed.com/oamfed/idp/initiatesso?providerid=https://saml.salesforce.com
  • Provide the IDP user credentials as given below and click on submit
 
  •  Hurray... Now you are authenticated against IDP and seamlessly SSO'd into Salesforce
  • During this SSO, OAM will generate a SAML2.0 standards based message including user details and send it to salesforce. On the other end, salesforce will receive this message 
    • validates the sender with details configured in idp partner profile
    • identifies the user information in saml message
    • Redirects user to the home page
  • We can view SAML2.0 message flowing from IDP to SP with the help of browser extensions like 'SAML tracer' in firefox.
  •  Following is the SAML message that is generated from IDP to SP in our scenario which has various details like
    • Issuer information
    • NameID policy
    • subject value
    • validity of assertion  
    • audience
  • Purpose of all these information is very well explained in the link https://docs.oasis-open.org/security/saml/v2.0/saml-core-2.0-os.pdf
 
  • That's all folks. In the future posts, I will post about various other features in Federated SSO using SAML2.0
Thanks for visiting..